Best API Security Testing Tools in 2026: 10 Tools Compared
Compare 10 API security testing tools across DAST, spec auditing, and runtime protection, including DastPilot, StackHawk, OWASP ZAP, Burp Suite, 42Crunch, Akto, and Escape.
Read article →DastPilot reads your OpenAPI/Swagger specification and uses AI in addition to traditional methods to plan and execute real security attacks against your API — uncovering OWASP API Top 10 issues including BOLA, injection, broken auth, and more.
Or try the live sandbox demo → No email or account required.
Legacy application scanners were designed for standard web page forms, not structured API endpoints. Testing your APIs with outdated scanners leads to developer friction and critical gaps.
DastPilot was built from the ground up to read API schema definitions directly, executing real attack traffic that adapts to query strings, authentication payloads, and parameter definitions.
Writing postman security scripts or setting up intercepting proxies takes weeks of security engineering hours.
Most scanners report alerts based on regex rules alone, without validating payloads or providing actual proof.
Common DAST vendors gate basic API ingestion behind expensive five-figure enterprise contracts, blocking startups.
No agents to install. No manual test writing. Point DastPilot at your OpenAPI spec and get a full vulnerability report in minutes.
Point DastPilot to your OpenAPI 3.x or Swagger 2.0 spec file or URL, or import a Postman collection (beta). We parse every endpoint, parameter, and schema automatically.
Our engine generates and fires real HTTP requests — fuzzing parameters, testing auth, probing for BOLA and injection across every endpoint.
Receive a detailed vulnerability report with exact payloads, CVSS scores, affected endpoints, and step-by-step remediation guidance.
DastPilot tests for every vulnerability category in the OWASP API Security Top 10 — automatically, on every scan, with real attack payloads.
Automatically tests broken object-level authorization by attempting cross-user resource access across all resource endpoints.
SQL, NoSQL, SSTI, command injection — DastPilot fuzzes every parameter with targeted payloads based on field types in your spec.
Tests JWT token tampering, expired token acceptance, missing auth headers, and privilege escalation paths.
Detects overly verbose error messages, missing security headers, and unsafe HTTP methods exposed unintentionally.
Identifies PII, secrets, API tokens, and sensitive fields returned in HTTP responses beyond what the specification declares.
Identifies when APIs accept unauthorized property modifications, preventing privilege escalation via parameter tampering.
A clean, evidence-first interface built for security engineers and developers alike. Every finding includes the exact payload, endpoint, and remediation steps.
| Risk Category | API Endpoint | Method | Severity |
|---|---|---|---|
| Broken Object Level Authorization (BOLA) | /v1/users/{userId}/profile | GET | CRITICAL |
| Mass Assignment | /v1/accounts/billing | PUT | HIGH |
| NoSQL Injection | /v1/products/search | GET | HIGH |
| SQL Injection | /v1/feedbacks | POST | HIGH |
Every open finding shows the OWASP category, affected endpoint, HTTP method, and severity — so your team knows exactly what to fix and where.
Developers get the exact request headers and payload triggered by the scanner alongside the leaked response, eliminating debugging ambiguity.
Context-aware API fuzzing that analyzes your API's structure and relationships to prioritize risk and find complex vulnerability chains.
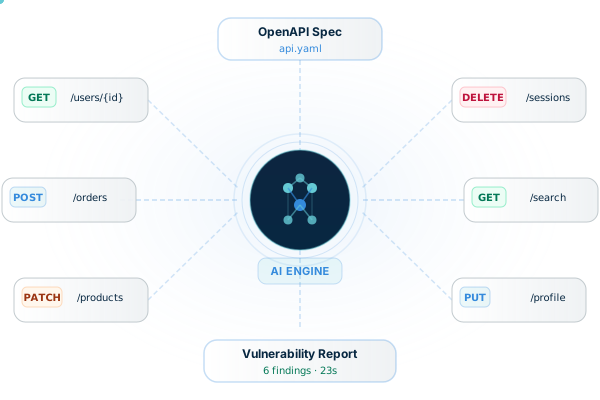
Instead of executing the same basic fuzzing parameters against every endpoint, DastPilot's AI Scan Planner parses schema structures and data models, then builds attacks around how an endpoint actually behaves.
Whether you are shipping your first MVP or managing compliance across AppSec teams, DastPilot adapts to your needs.
Ensure security compliance from day one without hiring a dedicated security specialist. Fast onboarding and clear dashboard statuses.
Validate vulnerability paths instantly. Zero guesswork with evidence-first reporting showing exact HTTP requests and responses.
Shift security testing left. Automate testing tasks directly inside existing repositories and pipelines, without overhead.
DastPilot maps every test to the OWASP API Security Top 10 so your reports speak the language your security team already uses.
Learn how to test the OWASP API Top 10, find BOLA and IDOR flaws, and choose the right tools for your team.
Compare 10 API security testing tools across DAST, spec auditing, and runtime protection, including DastPilot, StackHawk, OWASP ZAP, Burp Suite, 42Crunch, Akto, and Escape.
Read article →A phase-by-phase API penetration testing checklist covering discovery, authentication, authorization, input handling, business logic, rate limits, and reporting.
Read article →A practical walkthrough of all ten OWASP API Security Top 10 (2023) risks, with example requests, what a scanner can and cannot verify, and how to prioritize fixes.
Read article →One API definition (operation) from your OpenAPI specification. If your OpenAPI file contains 10 API definitions (e.g., GET /users, POST /orders, etc.), that counts as 10 APIs for billing purposes.
All APIs added within your first 30 days are free to scan with full access. After 30 days, billing begins at $2.00/API/month. No credit card is required to set up your account and start scanning.
DastPilot covers all 10 categories of the OWASP API Security Top 10, including BOLA/IDOR, broken authentication, injection attacks (SQL, NoSQL, SSTI), mass assignment, security misconfiguration, sensitive data exposure, and more.
Yes. There are no contracts, commitments, or lock-ins. You can delete active specs or deactivate billing directly from your DastPilot dashboard settings.
Yes. Import a Postman Collection v2.0 or v2.1 JSON export, or use the beta guided importer for Postman v3 folders. DastPilot suggests sign-in, test-account, and endpoint-access details for you to review. See the Postman security testing guide.
Yes. Create an API token, trigger a scan for an already-configured target from your pipeline, poll for the result, and fail the build on the severities you choose. Read API security testing in CI/CD for a recommended pipeline design.
ZAP and Burp Suite are general web scanners and proxies that need manual configuration to test API authorization. DastPilot is API-first: it models your roles and resource ownership, then checks every operation for BOLA, BFLA, and other OWASP API Top 10 risks on every scan. Compare them in DastPilot vs OWASP ZAP and Burp Suite alternatives.